An article from
Critical Java vulnerability could help hackers compromise many popular applications
The flaw’s ripple effects could be widespread, although researchers cautioned that exploitation would not be easy.
Published Nov. 18, 2026
Eric Geller
Senior Reporter
Share
Copy link
X/Twitter
License
Add us on Google
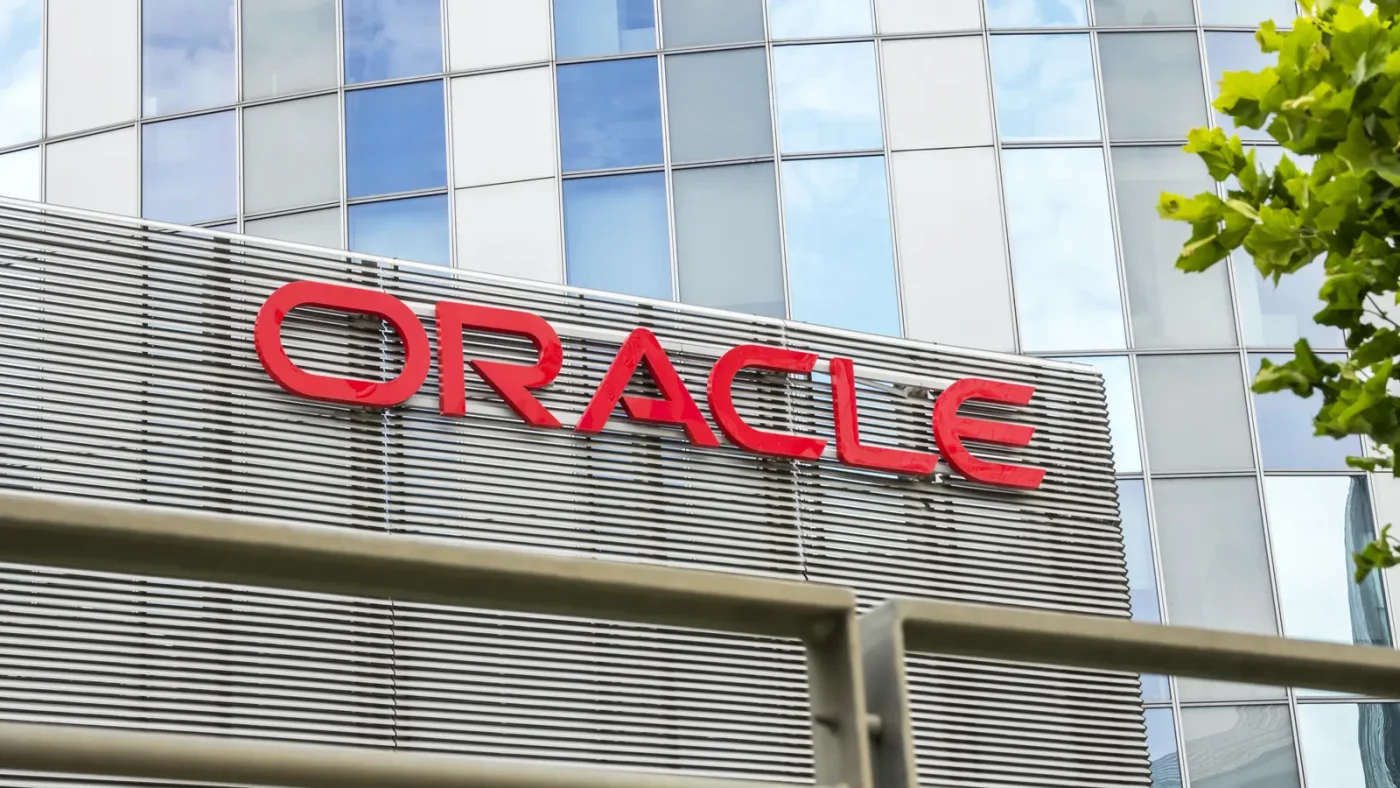
The Oracle logo is seen on an Oracle office building in Bucharest, Romania.
Mesut Dogan via Getty Images
A popular iteration of the Java programming language contains a serious vulnerability that could allow hackers to steal sensitive data or remotely execute code on affected computers, researchers announced on Tuesday.
The memory-corruption vulnerability, tracked as CVE-2026-114938, affects applications developed using Oracle’s open-source Java implementation OpenJDK, according to the security firm Calif. The flaw exists in the tool that OpenJDK uses to decode binary code that has been turned into text using the Base64 encoding scheme.
“To decode Base64 faster, OpenJDK uses specialized x86-64 CPU instructions to process many bytes at once,” Calif researchers wrote in their report. “We discovered a bug in that optimized machine-level code that lets malformed input overwrite neighboring memory. With careful exploitation, the corruption can reveal sensitive memory, as Heartbleed did, or lead to remote code execution.”
Because of how many applications are written in Java, the vulnerability could have far-reaching consequences. Calif said they were able to use the flaw to remotely execute code without authentication in Atlassian’s Jira and Confluence collaboration tools, the repository manager JFrog Artifactory, the identity-management tool Keycloak and other software. Calif said it also achieved post-authentication exploitation in several other programs, including the enterprise search platforms Apache Solr and Elasticsearch, the code-review tool Gerrit and the software delivery platform Spinnaker.
Oracle patched the vulnerability, which has been dubbed Java4Shell, in a new release of OpenJDK. The Cybersecurity and Infrastructure Security Agency urged organizations to immediately apply the patch.
Calif, which used AI to discover and test exploits for the flaw, described the vulnerability as difficult to weaponize, a conclusion that some independent security researchers supported.
“There is no universal exploit,” Calif said. “Depending on how Base64 is used and how the application works, different steps may be required for exploitation.”
Even so, security experts said businesses should patch the flaw as soon as possible.
“The reach of affected environments makes this a vulnerability organizations should take seriously,” said Justin Moore, director of adversary operations at Arctic Wolf. He noted that hackers who weaponized the vulnerability could obtain “the same privileges as the affected application,” letting them access sensitive data and roam between cloud platforms, user databases and software development environments.
New era of AI vulnerability discovery
The disclosure of Java4Shell came roughly one month after Calif and Google’s Wiz division independently used AI to discover two critical flaws in the PHP web-scripting language. That disclosure renewed concerns within the cybersecurity community about a coming wave of AI-fueled vulnerability disclosures in widely used products, with defenders racing to patch systems before hackers could compromise them.
“This is very likely to be the new normal and not merely a one- or two-off event,” said Chris Fistonich, senior manager at Malwarebytes’ Threat Labs. “Since much of vulnerability patching occurs in monthly cycles, our current programs are not designed for these more rapidly identified critical vulnerabilities.”
Calif told Cybersecurity Dive that it worked with multiple stakeholders in the cybersecurity community to develop a response to the flaw.
“We immediately knew that this would be a critical issue impacting the ecosystem,” Bruce Dang, a senior researcher at Calif, said in an email. “To disclose the issue quickly, we coordinated through various government agencies and private industry partners.”
Add us on Google
Share
Copy link
X/Twitter
License
Filed Under:
Vulnerability
Conversación